Cyber threats continue to grow in sophistication and frequency. Businesses are no longer asking whether they need advanced monitoring tools. They are asking how to implement them effectively. Security Information and Event Management systems, commonly known as SIEM, have become central to modern cybersecurity strategies.
Selecting the right managed security service provider with SIEM capabilities requires more than comparing feature lists. It involves understanding service scope, integration requirements, compliance demands, and long-term optimization. This guide outlines the key considerations to help organizations choose a future-ready security partner.
People Also Ask
What is SIEM in cybersecurity?
SIEM stands for Security Information and Event Management. It collects and analyzes security data from multiple systems to detect potential threats.
Why use a managed security service provider for SIEM?
Managed providers offer continuous monitoring, configuration expertise, and structured response processes that improve detection and reduce false alerts.
Is managed SIEM better than self-hosted SIEM?
Managed SIEM often benefits organizations without dedicated security teams by providing expert oversight and around-the-clock monitoring.
How does SIEM support compliance?
SIEM platforms centralize log data and generate reports that help demonstrate regulatory adherence and audit readiness.
Scope of Cybersecurity Services
A comprehensive cybersecurity company delivers more than monitoring software. Core offerings typically include network protection, endpoint security, vulnerability management, incident response, and compliance support.
When evaluating providers, confirm whether SIEM is integrated into broader managed security services or offered as a standalone tool. Security becomes more effective when monitoring, response, and infrastructure management operate under a unified strategy.
Organizations should also assess whether the provider offers strategic advisory services. Risk assessments, policy development, and ongoing security reviews strengthen long-term resilience.
Understanding SIEM
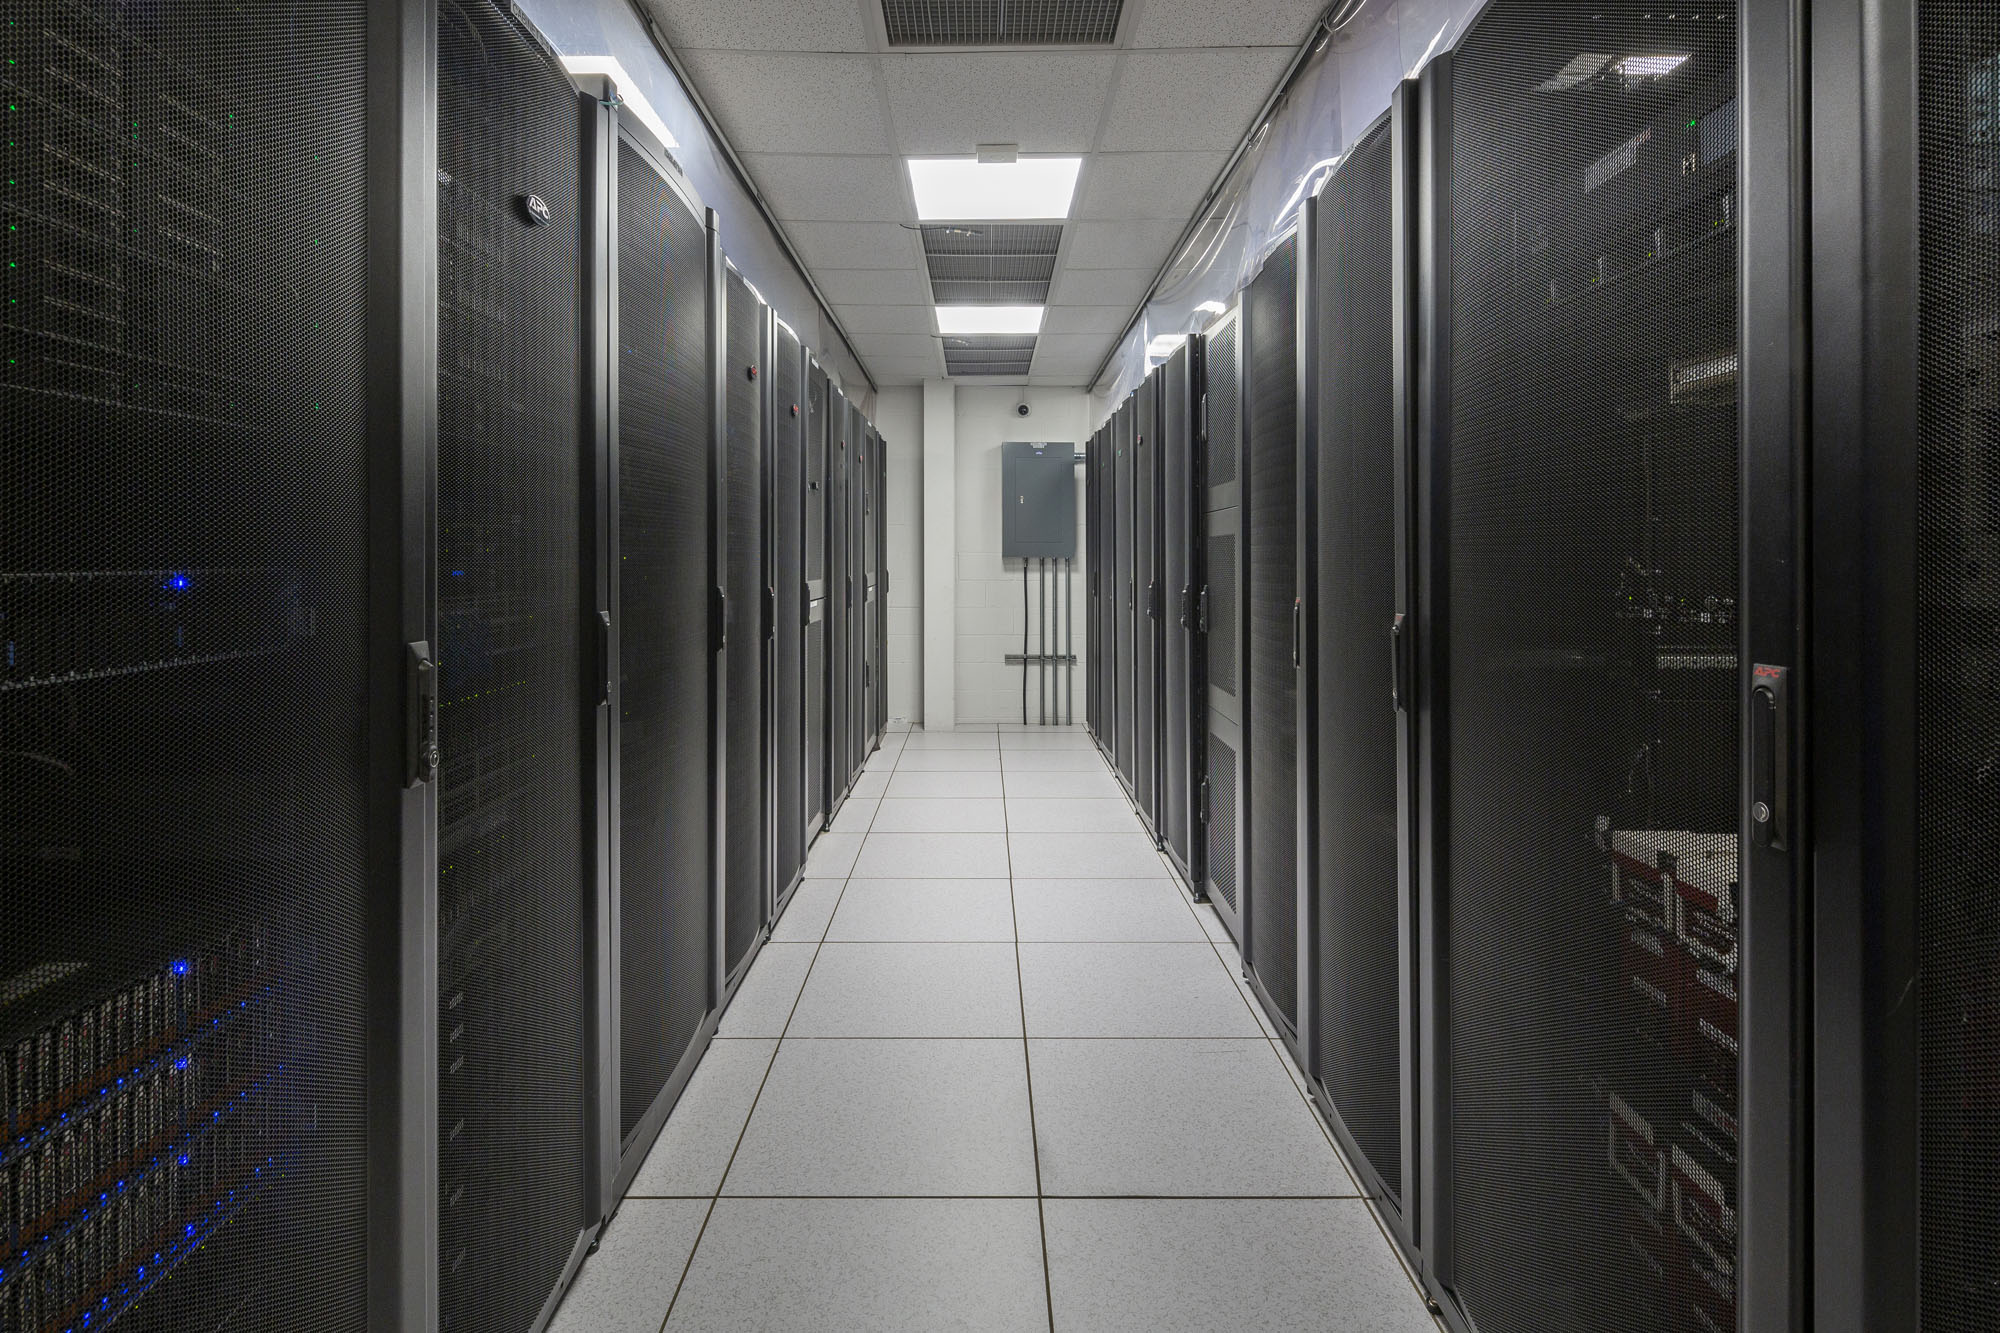
SIEM platforms collect and analyze security data from across the IT environment. Logs from servers, firewalls, endpoints, applications, and cloud systems are aggregated in centralized dashboards.
The goal is to quickly identify suspicious activity. SIEM tools correlate events, detect anomalies, and trigger alerts when predefined thresholds are exceeded.
Without proper configuration and continuous oversight, however, SIEM systems can produce excessive alerts or miss subtle threats. This is why many organizations rely on a managed security provider to configure and maintain the system effectively.
Managed vs. Self-Hosted SIEM
Self-Hosted SIEM Offers Direct Control
Some organizations choose to deploy and manage SIEM internally to maintain direct control over configurations, policies, and data handling. This model enables internal security teams to customize alert thresholds, correlation rules, and reporting structures to meet specific operational requirements. Companies with mature security operations centers often prefer this approach because it aligns closely with internal governance frameworks and established workflows.
However, full control also means full responsibility. Internal teams must manage deployment, integration with existing systems, log ingestion, storage optimization, and ongoing rule refinement. Without dedicated expertise and round-the-clock monitoring, self-hosted SIEM environments can become underutilized or generate excessive false positives.
Managed SIEM Transfers Operational Burden
A managed SIEM model shifts operational responsibility to a specialized external team. The managed security service provider oversees configuration, system updates, log correlation, alert triage, escalation procedures, and structured reporting.
This model ensures continuous monitoring without requiring internal staffing expansion. Providers typically operate with predefined workflows and escalation paths that streamline threat detection and containment. By leveraging experienced analysts, organizations benefit from structured oversight and faster response cycles.
Resource Efficiency and Reduced Staffing Strain
For businesses without a dedicated security operations center, managed SIEM reduces the burden on internal IT teams. Instead of hiring and training specialized security analysts, organizations gain access to an established team with defined processes and monitoring tools.
This approach supports operational continuity while allowing internal staff to focus on strategic initiatives rather than continuous alert management.
Choosing Based on Risk Tolerance and Expertise
The decision between self-hosted and managed SIEM ultimately depends on internal capabilities and risk appetite. Organizations with mature security teams may prefer direct oversight. Others may prioritize scalability, predictable costs, and structured monitoring through managed services.
Integration with IT Environment
SIEM systems must integrate seamlessly with existing infrastructure. This includes cloud platforms, on-premises servers, network devices, and enterprise applications.
Effective integration ensures comprehensive visibility. Partial integration can leave gaps that attackers exploit.
When assessing managed security services, request details on the provider’s integration experience. Providers should demonstrate familiarity with diverse environments and the ability to onboard new systems efficiently.
Scalability also matters. As businesses adopt additional cloud services or expand operations, SIEM coverage should expand without major disruption.
Evaluating Providers
Selecting a cybersecurity partner involves careful due diligence. Evaluate experience, response procedures, staffing models, and reporting transparency.
Ask how alerts are triaged and escalated. Confirm whether monitoring is continuous. Review service level agreements that define response times and accountability.
A strong managed security provider will offer documented workflows, regular reporting, and structured communication channels. Transparency strengthens trust and improves executive visibility into risk posture.
Compliance and Reporting
Regulatory frameworks across industries require detailed documentation and audit readiness. SIEM platforms support compliance by maintaining centralized logs and generating structured reports.
However, reporting effectiveness depends on proper configuration and review. Managed providers translate technical logs into executive-level summaries that align with compliance expectations.
Organizations in regulated sectors should verify that their chosen provider understands relevant privacy and industry standards and can demonstrate compliance support capabilities.
Ongoing Optimization
Cybersecurity is not static. Threat landscapes evolve, new vulnerabilities emerge, and business environments change.
An effective SIEM implementation requires continuous tuning. Alert thresholds must adapt to operational patterns. False positives should be reduced while maintaining sensitivity to real threats.
A reliable managed security service provider conducts regular reviews, adjusts detection rules, and refines monitoring strategies. Ongoing optimization ensures that SIEM remains a proactive defense tool rather than a reactive alert system.
Selecting a Future-Ready Security Partner
Choosing a cybersecurity services company with SIEM capabilities requires a structured evaluation of service scope, integration expertise, compliance readiness, and ongoing optimization practices.
Organizations that align with an experienced managed security services partner gain improved visibility, faster incident response, and stronger audit readiness.
Pathway Communications delivers comprehensive cybersecurity strategies through its solutions, integrating SIEM, infrastructure oversight, and compliance alignment.
To build a resilient security framework supported by a trusted managed security provider, contact us and speak with our team about strengthening your digital defense posture.